
DOD IG warns military staff to remove sensitive information from tech in Afghanistan withdrawal
The Department of Defense’s oversight body has warned military personnel they must wipe sensitive health and medical data from technology being returned as part of the U.S. withdrawal from Afghanistan.
In a report, the Inspector General (IG) reiterated rules that state all personally identifiable information must be removed from equipment including medical equipment, laptops and cell phones.
According to the IG, this is crucial both to prevent civilian and military records such as health and service records from falling into the wrong hands. The oversight body said also that officers must keep accurate records of technology that is returned as part of the withdrawal process.
In prior audits of military base equipment in Afghanistan, the IG found that the protocol for clearing information from equipment was not always being followed. In one case a device used to protect soldiers from improvised explosive devices was left showing sensitive location data.
“Unless equipment is properly processed by unit personnel before turning it into redistribution property assistance team personnel, there is a risk of theft and compromise of sensitive information,” the report said.
In May, DOD officials acknowledged that some U.S. military equipment could end up in the hands of Taliban fighters, but said military planners were using the time left until the pullout is complete to minimize the threat.
In February last year, the U.S. and the Taliban signed a conditional agreement to remove all U.S. forces from Afghanistan by April 2021. The military mission is set to conclude on August 31.
US Indian Health Service to replace health information system
The Indian Health Service is looking for electronic health record (EHR) vendors to replace the outdated health information system it and many tribal and urban American Indian healthcare organizations use, according to a draft statement of objectives (SOO).
Part of the Department of the Health and Human Services, IHS intends to award a 10-year indefinite delivery, indefinite quantity Health IT (HIT) Modernization Program contract with time-and-materials and firm-fixed-price task orders.
IHS developed the Resource and Patient Management System (RPMS) internally to support everything from patient registration to billing and pull from hundreds of databases nationwide. But recent advances in HIT and changes in regulations — as well as the decision of partner agency the Department of Veterans Affairs to move to a commercial off-the-shelf (COTS) solution — have IHS looking to do the same.
“IHS seeks HIT solutions that use innovative, next generation technologies and incorporate best practice clinical and business processes for improved health care outcomes,” reads the SOO. “The scope of capabilities and services touched by the IHS HIT modernization initiative is broad.”
Services include cradle-to-grave primary care, prenatal care, behavioral health, dental, eye care, physical therapy, and telehealth for American Indian and Alaska Native patients.
IHS wants a set of HIT COTS solutions that improve patients’ access to those services and their health information, quality of care, and health status. The agency is also looking to improve interoperability and information sharing across the American Indian health system and private and government partners, as well as security.
For that reason solutions must comply with the Federal Risk and Authorization Management Program, Federal Information Security Modernization Act, National Institute of Standards and Technology‘s Special Publication 800-53, recent cybersecurity executive order, and Health Insurance Portability and Accountability Act.
IHS anticipates vendors may face challenges meeting the diverse requirements of its tribal partners, as well as reporting requirements at the various levels of government.
The agency seeks vendor feedback on the requirements in its draft SOO and their capabilities, according to a request for information (RFI). Interested vendors have until 10 a.m. EDT on Aug. 19 to respond to the questions in the RFI.
NIST looks to perform AI, nanotechnology lab-to-market study
The National Institute of Standards and Technology intends to negotiation a contract for an artificial intelligence and nanotechnology lab-to-market (L2M) study to the Institute for Defense Analyses, according to a notice issued Aug. 3.
NIST wants to accelerate the commercialization of federally funded AI and nanotechnology research and development out of the Science and Technology Policy Institute.
The Institute for Defense Analyses administers STPI, a federally funded R&D center (FFRDC) that supports the White House Office of Science and Technology Policy in making L2M decisions.
NIST believes the Institute for Defense Analyses is the only vendor capable of performing the study because private companies may benefit “unfairly” from access to government information out of STPI or attempt to steer recommendations in their favor, according to the notice.
The Institute for Defense Analyses has history broadly assessing the federal technology transfer landscape and performing agency-specific analyses of early investments in R&D and commercialization efforts.
NIST may opt to compete the contract based on responses to its notice, due 8 a.m. EDT on Aug. 15.
Cyberspace Solarium Commission warns over slow progress on supply chain risk
The landmark Cyberspace Solarium Commission warned Thursday in an annual report that major barriers remain over the designation of cybersecurity responsibilities under the Defense Production Act (DPA).
In its initial report, published in March last year, the commission called on the federal government to use the DPA to foster domestic production of critical technology and components, and to ensure resources are available if foreign supply chains are disrupted.
Under the Defense Production Act, the federal government can invoke the authority to compel the private sector to prioritize certain contracts, as has occurred during the COVID-19 pandemic with companies such as 3M being compelled to produce masks and other medical equipment.
The report explains that regarding cybersecurity responsibilities related to the DPA, the commission “has encountered significant pressure against this recommendation, which is one of the four that face known significant barriers to implementation,” as it expected.
Other areas for concern identified in the annual report on implementation include progress in the creation of permanent select committees on cybersecurity in the House and Senate.
The report found also that major obstacles will need to be overcome before a national law on data security and privacy protection can be passed.
The latest document represents a progress update on the implementation of recommendations from the initial Cyberspace Solarium Commission report. Of recommendations included in the initial report, 22% have so far been implemented, 13.4% are nearing implementation, and 43.9% are identified as being “on track.” However, progress has been limited on 15.9% of proposals, and significant barriers remain in enacting 4.9% of recommendations.
However, the report also highlighted a number of core recommendations that so far have been achieved by the White House, including the creation and appointment of the role of National Cyber Director, provisions to strengthen the Cybersecurity and Infrastructure Security Agency, the codification of sector risk management agencies, and the launch of a joint cyber planning office.
“The Commission is proud of its progress but recognizes that in order to determine where we go next in cybersecurity, we must be clear eyed about what is not working,” the report said.
The commission is chaired by Sen. Angus King, I-Maine, and Rep. Mike Gallagher, R-Wisc.
GAO to decide WildandStormy bid protest outcome by Oct. 29
The Government Accountability Office will decide the outcome of a bid protest filed by Microsoft over a billion-dollar cloud procurement involving the National Security Agency by Oct. 29.
A GAO spokesperson confirmed to FedScoop that the agency had received a complaint from the tech giant, and outlined a timeline for the bid protest process.
Under procurement rules, GAO will issue an initial report in response by Aug. 20, and Microsoft will have 10 days to respond.
The dispute is understood to relate to a $10 billion cloud contract, which according to sources was awarded to Amazon. It is known in the federal IT community as WildandStormy.
“NSA recently awarded a contract for cloud computing services to support the Agency. The unsuccessful offeror has filed a protest with the Government Accountability Office (GAO),” a spokesperson for the NSA told FedScoop. “The Agency will respond to the protest in accordance with appropriate federal regulations.”
Details of the bid protest were first reported by Washington Technology.
A spokesperson for Microsoft confirmed the protest, saying: “Based on the [award] decision we are filing an administrative protest via the Government Accountability Office. We are exercising our legal rights and will do so carefully and responsibly.”
News of the bid protest comes after the Department of Defense last month announced that its Joint Enterprise Defense Infrastructure (JEDI) cloud contract would be scrapped, following a nearly two-year legal dispute waged by Amazon protesting the contract’s award to Microsoft. It has been replaced with the Joint Warfighter Cloud Capability acquisition, which the department intends to issue as a multi-cloud, multi-award contract.
Forthcoming Commerce enterprise IT contract could total $1.5B in task orders
The Department of Commerce intends to issue an enterprise IT contract worth as much as $1.5 billion in task orders over 10 years, according to a draft request for proposals posted to SAM.gov.
The Commerce Acquisition for Transformational Technology Services (CATTS) contract covers six task areas: chief information officer support, digital document and records management, managed service outsourcing and consulting, IT operations and maintenance, IT services management, and cybersecurity.
DOC‘s CIO office wants to use cloud platforms to deliver as-a-service offerings to its agencies to meet their business needs.
“The department is moving in a direction of minimizing the capital investments needed every three-to-five years for a technology refresh of obsolete infrastructure equipment and hardware,” reads the performance work statement. “Utilizing IT as a service, the DOC can position itself to meet the strategic goals, deliver its missions, and be recognized as a leader within future administrations and the federal enterprise in its use of information technology.”
The indefinite delivery, indefinite quantity contract is expected to have a maximum value of $1.5 billion and has a base period of one year and nine option years. Task orders may be issued on a firm-fixed-price of time-and-material/labor hour basis and may be performance based
DOC wants contractors that can reduce its on-premise footprint in favor of the cloud as much as possible.
Within the six task areas, DOC anticipates purchasing artificial intelligence, DevSecOps and FITARA program support services in addition to as-a-service offerings. Additional task work could include Cybersecurity Maturity Model Certification support.
DOC plans to hold a virtual industry day for all vendors on August 12 and another for minority-owned small businesses on August 16 to brief interested contractors on its vision, procurement strategy and timeline for CATTS, as well as solicit industry feedback prior to releasing the final solicitation.
The case for establishing an interoperable zero trust foundation for JADC2
Dan Schaaf is Senior Solutions Director and Army Sector CTO for GDIT, with more than 30 years’ experience implementing IT solutions and enterprise architecture for the U.S. Army and in the defense sector.
Defense officials for much of the past decade have recognized that future conflicts will require leaders to make decisions within minutes, or even seconds, and that the days of prolonged analysis are no longer an option. That concern was clearly spelled out more than three years ago by the National Defense Strategy Commission, which concluded that the state of the military’s Command and Control (C2) systems had “deteriorated” relative to potential competitors; and that the concept of a Joint All-Doman Command and Control (JADC2) network was clearly needed.
For all of the many strengths each of the services brings to the nation’s common defense, their central weakness remains the fact that the Air Force, Army, Marine Corps, Navy and Space Force each rely on separate and incompatible information networks. This reality leaves the Defense Department, and its ability to effectively defend and protect America’s interests, increasingly at risk.
Dan Schaaf, Senior Solutions Director and Army Sector CTO, GDIT
The vision for JADC2 is to create a single network to connect sensors to weapons systems and deliver information advantage at the speed of relevance. Currently the services are developing transformational IT capabilities tailored to their own needs, focused on cloud, data platforms and the implementation of zero trust. But for JADC2 to achieve warfighting capability, it is critical that DOD leaders put a stake in the ground and insist on establishing a set of common, foundational capabilities that will ensure that mission critical data can move across the DOD securely; data can be shared and analyzed where and when it’s needed; and the data can be trusted.
It is broadly accepted that a DOD-wide implementation of zero-trust security is foundational to the success of JADC2. But if DOD leaders do not establish critical zero trust capabilities, there are very real risks that as each of the services develop their own service-centric cloud environments and data platforms, they will also implement service-centric zero-trust capabilities. Ultimately this will increase the complexity of the operating environment and short circuit the DOD’s ability to access and exploit the relevant data and services required for joint and multi-domain operations.
To that end, DOD leaders should establish a foundational set of common zero trust capabilities and then require the services, the defense industry and our mission partners to use and ideally leverage those foundational zero trust capabilities.
The value of establishing a foundational DOD zero trust capability can be found in examining the use case of DOD’s decision to establish a PKI root certification authority for all identity and access management initiatives. By mandating the use of a common PKI root certification, the Defense Department created an environment that maintained and promoted cross-service interoperability and trust while still enabling each service to individually deploy identity and access management services.
Conversely, we can also learn from the DOD deployment of network directory services where they did not mandate the use of a trusted root. Though that deployment occurred more than two decades ago, the DOD still faces challenges to effectively federate and consolidate the multiple network domains that were created within the DOD, and which continue to significantly hamper efforts to develop a unified DOD network.
A way forward for cross-DOD zero trust
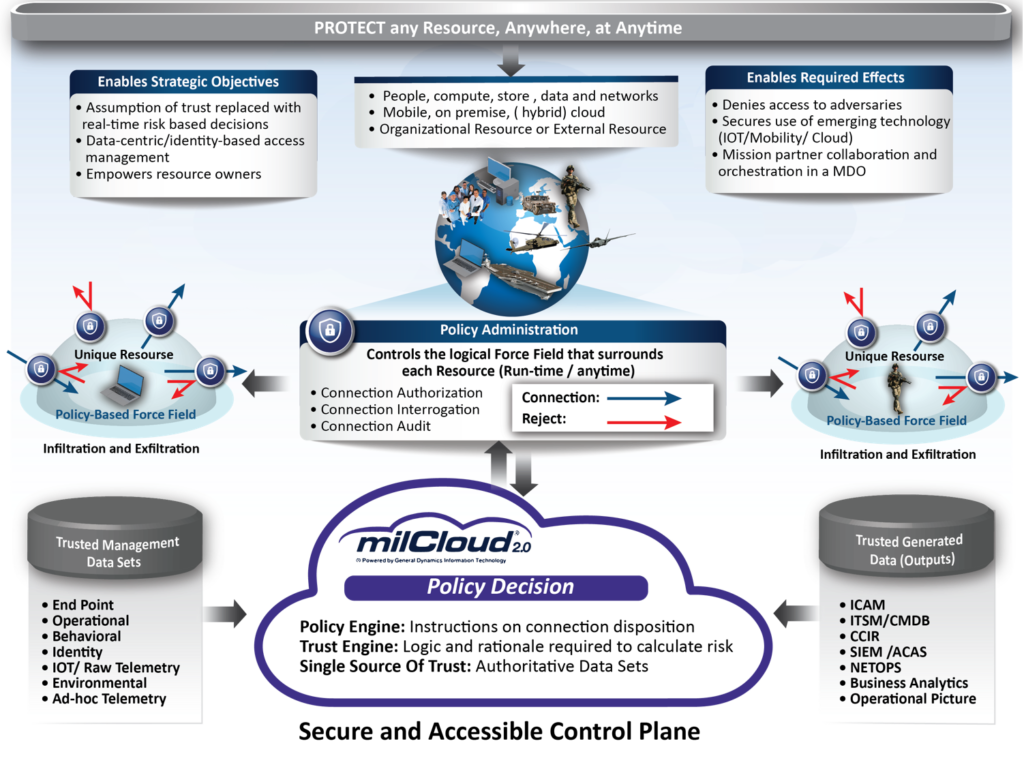
To further illustrate this point and conceptually describe what foundational zero trust capabilities should be developed, Figure 1 below is the GDIT zero trust architecture which demonstrates two key innovative concepts: 1) federated security enforcement and 2) centralized and data driven policy decision capability
Figure 1: GDIT Zero Trust Architecture
Source: GDIT
Along the center of Figure 1 is a “Policy Administration” capability that we propose. It represents the federated security enforcement devices which control the connection to resources. These are typically devices like firewalls or other access control mechanisms and are distributed throughout the enterprise today; but they also represent new and emerging zero-trust technologies that provide micro-segmentation of a network or dynamically establish software defined perimeters around resources.
Our recommendation for a foundational zero trust capability is the “Policy Decision” capability (along the bottom of Figure 1) which integrates a policy engine, a trust engine and a single source of truth. When centrally developed and managed, this capability will enable the DOD to incrementally deploy zero trust capabilities as well as integrate existing security enforcement devices.
To develop the “Policy Decision” capability, it’s critical that the DOD establishes the ground rules for what constitutes authoritative data — and ultimately lay the foundation for an enterprise-wide authoritative data environment. It’s also crucial that security enforcement systems working at machine speeds can discern what’s authoritative and what’s not in real time. That’s especially important as artificial intelligence within the trust engine is processing the data to determine relative risk and thresholds so that it is delivering the highest quality input to the policy engine that will synchronize the security enforcement devices and technologies.
Logically, the zero trust foundational capabilities should be delivered from a DOD cloud infrastructure to ensure the zero-trust management platform can operate securely and is also accessible by each service, the defense industry, mission partners and their data systems. Commercial clouds offer significant advantage for general purposes, but for joint operations, data must be integrated and served up without the friction arising from such factors as ingress and egress costs, data locality challenges or stovepipes resulting from disparate multi and hybrid cloud architectures among the military departments. Likewise, it makes sense for DoD’s own standardized capability for policy enforcement in support of JADC2 to be held in reserve, and not have different, even competing access regimes across the services.
A DOD Enterprise cloud is especially important for this use case. For those reasons, we are recommending DISA’s milCloud 2.0 cloud and contract as the location for the zero trust foundational capabilities. It can host the same innovative capabilities that leading edge companies host in the commercial cloud today; and it is located securely on DISA’s premises and inside DOD’s information networks. It is also FedRAMP-certified to meet DOD Impact Level 5 security ratings (and soon to be IL-6 certified) and it’s already accessible by all DOD components and authorized DOD partners.
By putting the foundational zero trust capabilities in place now and establishing a secure and accessible control plane for zero trust, DOD has a better chance of ensuring that they can protect any resource, anywhere and at any time. And just as importantly, it will accelerate warfighter capability by ensuring data from sensors, users and applications operating on and across JADC2 can be trusted and be used more universally.
Why SD-WAN takes on greater importance in hybrid IT environments
As government organizations continue to expand their hybrid IT environments and adopt zero trust security practices, agency leaders will need to move away from traditional wide area networks (WAN) and adopt newer software-defined networking (SD-WAN) solutions, says a long-time federal security expert in a new report.
That transition takes on new importance in light of the May 2021 White House executive order outlining new requirements to embed stronger security controls embedded into federal IT enterprise networks, including implementing zero-trust security architecture within the year.

Read the full report.
The executive order follows more than a year of fast-tracked modernization initiatives by federal and state agencies to support their remote workforce, including the deployment of online as-a-service platforms, digital voice and video applications and robotic process automation.
“As agencies integrate more digital services, they are looking to tap into the dynamic connectivity of hybrid IT environments. [However,] overlay security tools are no longer capable of adapting to these environments,” said Jim Richberg, field CISO at Fortinet and former National Intelligence Manager for Cyber in the Office of the Director of National Intelligence.
The uptick in demand for faster, more user-focused and secure tools require infrastructure upgrades to provide higher bandwidth, scalability, flexibility and integrated security. Software-defined wide area networking (SD-WAN) is proving to be one of the fastest-growing segments of the network infrastructure which can provide all these things, according to information from Gartner cited a new Scoop News Report, underwritten by Fortinet and immixGroup,.
Integrating security and networking has never been more important, said Richberg, and he pointed to research from Fortinet which showed ransomware instances that arrived through the endpoint increase by 700% in the second half of 2020.
“Even with multifactor or endpoint security solutions, the reality is that organizations still don’t know what is going in the environment,” he said, adding that with cyberthreats today, organizations can’t afford to function as if the network and security are separate. These two functions are increasingly converged, and SD-WAN is able to treat it as such.
The report points to several key benefits of SD-WAN networking. Most importantly, it supports zero trust strategies, including the ability to validate devices and users on the network, close visibility gaps in a hybrid environment and automate security policy updates across the network. Additionally, it is available for federal agencies to purchase under the Enterprise Infrastructure Solutions (EIS) contract task order.
According to Richberg, a best-of-breed SD-WAN solution tightly integrates networking connectivity and security, meeting multiple networking needs at once.
The report highlights five ways that advanced SD-WAN solutions, like those from Fortinet can be “self-healing,” using automation.
The report also delineates why not all SD-WAN solutions deliver the same level of security capabilities. More robust solutions, for instance, embedded with tried-and-tested artificial intelligence and machine learning technology, give agencies the ability to achieve a common operating picture of their networks and respond to threats more quickly.
“Adding AI to policy-driven automation allows the system to validate users and deal with low level security anomalies automatically, which frees agency employees to focus on those more complex tasks where they need to exercise their skill and judgement,” the report concluded.
Read more about why transitioning to secure SD-WAN is the right choice for government agencies.
This article was produced by Scoop News Group and sponsored by Fortinet and immixGroup.
OMB gives agencies 60 days to identify critical software and begin securing it
The Office of Management and Budget has given federal agencies 60 days to identify all their critical software in use or being acquired and a year to secure it, according to a memo issued Tuesday.
OMB directed agencies to focus on securing standalone, on-premise software performing “security-critical” functions or posing “significant potential for harm” if compromised, during the initial implementation phase of critical software guidance released by the National Institute of Standards and Technology on July 8.
The latest mandate comes after President Biden on May 12 issued an executive order titled Improving the Nation’s Cybersecurity, which required NIST to define critical software to help agencies prevent its unauthorized access, secure data and quickly respond to threats.
“The United States faces increasingly sophisticated malicious cyber campaigns that threaten the public sector, the private sector and ultimately the American people’s security and privacy,” said the memo. “The federal government must improve its efforts to detect, identify, deter, protect against, and respond to these campaigns and their perpetrators.”
Phase 1 of implementing NIST’s guidance includes software handling: identity, credential and access management; operating systems, hypervisors and container environments; web browsers; endpoint security; network control; network protection; network monitoring and configuration; operational monitoring and analysis; remote scanning; remote access and configuration management; and backup/recovery and remote storage.
NIST will update its guidance as needed to launch subsequent phases covering additional software categories selected by the Cybersecurity and Infrastructure Security Agency, which agencies will have one year from release to address.
Subsequent phases will cover: software that controls access to data; cloud-based and hybrid software; software development tools like code repository systems, testing software, integration software, packaging software, and deployment software; software components in boot-level firmware; and software components in operational technology (OT).
NIST defined critical software as that which, or is dependent upon software that:
- is designed to run with elevated privileges or manage privileges,
- has direct or privileged access to networking and computing resources,
- is designed to control access to data or operational technology,
- performs a function critical to trust, or
- operates outside of normal trust boundaries with privileged access.
Some cybersecurity experts found NIST’s definition narrow at the time and feel Phase 1’s focus on security products — rather than industrial control, financial, health and election systems — goes against the spirit of the cybersecurity executive order.
“I’d say software is critical if compromised it would cause significant loss of human life or irreparable infrastructure damage or extensive financial harm,” Jeff Williams, chief Technology Officer at Contrast Security, told FedScoop. “Maybe undermining democracy if it’s an election system, but the definition as it’s written right now doesn’t touch any of those systems.”
It is possible NIST was just trying to get a definition out the door or faced pressure from system integrators reluctant to add additional security controls to the software they sell the government, Williams added.
Of the systems Williams wants addressed, only OT was mentioned in OMB’s memo as software to be targeted in a later phase — though it does leave room for agency discretion.
“Agencies should keep in mind that the measures identified in the guidance from NIST are not comprehensive,” reads the memo. “Their adoption may not eliminate the need to implement additional security measures to satisfy requirements and objectives that lie outside the scope of the NIST guidance.”
DOD awards $1B contract to Peraton to counter misinformation
The Department of Defense has awarded a task order worth up to $979 million over a five-year period to Peraton to counter misinformation from U.S. adversaries.
The contractor will provide services to U.S. Central Command and its mission partners with operational planning, implementation and assessment services.
Peraton has undertaken such work for Central Command since 2016 under its counter-threat messaging support program, and according to the company, the latest contract represents a doubling of work already scheduled to be carried out under the program.
Commenting on the contract, Tom Afferton, president of Peraton’s cyber missions sector, said: “Since 2016, Peraton has executed campaigns to promote regional security and stability. Our ability to provide the U.S. government with insight, expertise, and influence helps ensure the safety of Americans, our allies, and the more than 550 million people under U.S. Central Command’s area of responsibility, spanning three continents and 20 nations.”
The award comes after Peraton earlier this month won an IT infrastructure contract from the Department of Veterans Affairs, which could be worth up to $497 million over seven years.
The Virginia company will provide infrastructure-as-a-managed service for storage and computing infrastructure facilities across the U.S. and globally. Announcing the award, Peraton said it will deliver an enterprise-scale solution that integrates on-premise infrastructure with the VA’s enterprise cloud architecture.
Since 2016, the Department of Defense has worked with private sector contractors to counter-messaging from U.S. adversaries including ISIS across media, including social networks.
The fiscal 2016 defense authorization bill included a clause stating that the secretary of Defense should develop “creative and agile concepts, technologies, and strategies” across all available media to counter and degrade the ability of adversaries to persuade, inspire and recruit.