CFPB can’t say if it secured IT assets at regional offices it vacated, OIG says
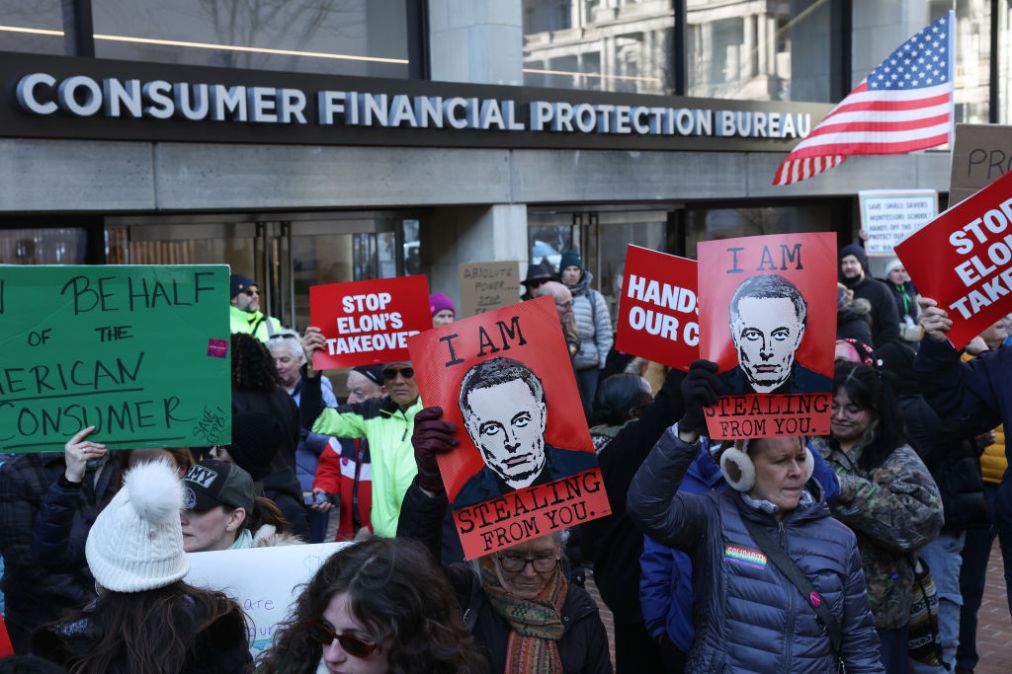
The Consumer Financial Protection Bureau isn’t sure if it properly secured IT assets at four regional office spaces whose leases were terminated last year, an oversight that a watchdog said could have exposed the private information of individuals and businesses.
A management alert published last week by the Federal Reserve’s Office of Inspector General detailed how technology hardware at CFPB offices in Atlanta, Chicago, New York and San Francisco slipped through the cracks as the Trump administration looked to downsize the agency’s footprint.
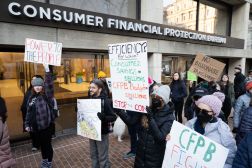
In February 2025, the CFPB and General Services Administration agreed to cancel the regional office leases, with GSA taking over for the buildings’ physical security and the consumer agency retaining ownership and responsibility for the IT assets that remained.
A CFPB official told the Fed OIG that the agency stopped paying fees for network connectivity in September 2025, but six months later, it still hadn’t “completely vacated the regional offices.” And as of last month, the CFPB hadn’t verified if the IT equipment had been “appropriately secured” and said it had “no approved plan or time frame for verifying the security of hardware assets” at the sites, citing ongoing litigation and lack of approvals for travel.
“By not verifying the security of these assets, which were left in four former regional offices over 18 months ago, the CFPB has no way of knowing whether the hardware assets, or the sensitive data that may be stored on them, have been accessed, modified, or removed by unauthorized individuals,” the watchdog wrote.
Potentially sensitive data, housed in various CFPB databases, could have come from consumer complaints, financial information and confidential supervisory records on banks and other financial institutions. Exposing that data would “undermine public trust, and compromise the CFPB’s ability to enforce consumer financial laws,” the alert said.
The CFPB agreed with the OIG’s recommendation to ensure that all hardware assets at the regional offices are accounted for and secured. And the agency’s chief information officer said in a letter to the watchdog that a “full, site-by-site IT decommissioning” of those four offices “has already begun.”
But the agency pushed back on “the nature of the assets in those offices,” writing in the response letter that “no databases containing sensitive data are housed in the regional offices.” There was “no basis” for the Fed OIG’s assertion that sensitive information from individuals or businesses was at risk, the CIO added.
The Fed OIG didn’t respond directly to the CFPB’s pushback, but said it would share more information in its upcoming Federal Information Security Modernization Act report for the agency.
“The actions described by the CFPB appear to be responsive to our recommendation,” the alert said. “We will follow up to ensure that the recommendation is fully addressed.”